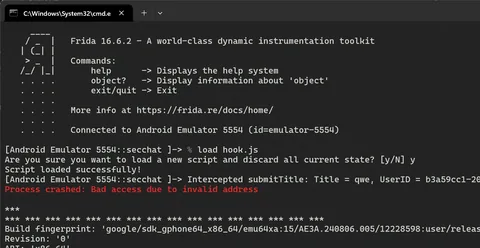
紀錄一下攔截某APP的封包流量透過中間人攻擊
紀錄一下攔截某銀APP的封包流量透過中間人攻擊 紀錄一下脫機的過程,因為一些因素所以,沒有追完全全部,等最近有空再說 反正主要目的就是假設一個APP 我要提取目標其中功能,我是否可以透過 HOOK的方式 將所有APP 流程轉成 API 也就是我要攔截 APP的 HTTPS 的流量 得到 請求的 request 然後在透過 攔截 app 的 簽章加密的 function 試圖找出…
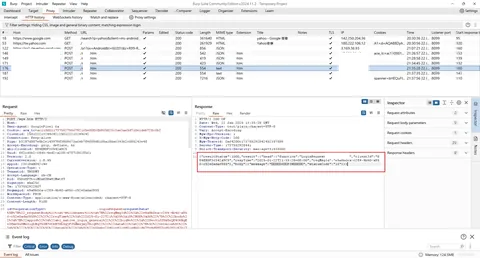
LABEL / Frida
4 posts
紀錄一下攔截某銀APP的封包流量透過中間人攻擊 紀錄一下脫機的過程,因為一些因素所以,沒有追完全全部,等最近有空再說 反正主要目的就是假設一個APP 我要提取目標其中功能,我是否可以透過 HOOK的方式 將所有APP 流程轉成 API 也就是我要攔截 APP的 HTTPS 的流量 得到 請求的 request 然後在透過 攔截 app 的 簽章加密的 function 試圖找出…
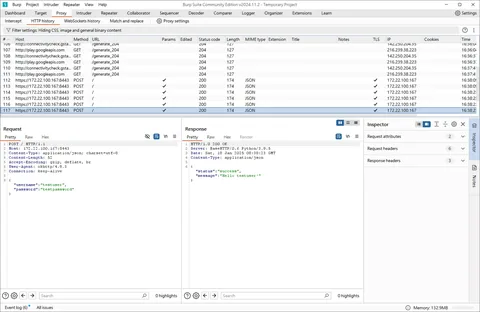
frida + burp Intercept https traffic det to cert openssl x509 -inform DER -in test -out burp_cert.crt adb push .\burp_cert.crt /data/local/tmp adb shell mv /data/local/tmp/burp_cert.crt /sdc…
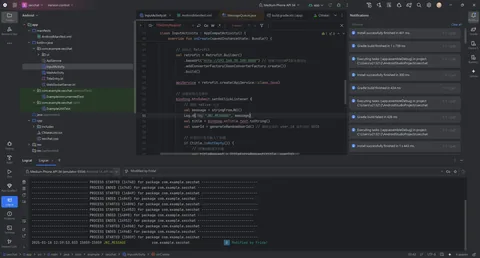
using ida pro debug apk & hook native function example 將IDAPro\dbgsrv內部的gdb server 透過 adb 傳到 虛擬機或手機內部 code Copy adb push android_x64_server /data/local/tmp adb shell su cd /data/local/tmp ch…
use magisck root image && frida example magisck 對 android 虛擬機進行root https://systemweakness.com/rooting-emulator-and-installing-magisk-c3cbd34ec436 這邊直接指向 android 虛擬機 ram disk.img刷入即可 code Co…